


[Full-Version] 2026 New Preparation Guide of Salesforce Salesforce-MuleSoft-Developer-II Exam
Salesforce-MuleSoft-Developer-II Practice Exam - 62 Unique Questions
Salesforce Salesforce-MuleSoft-Developer-II Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 35
Refer to the exhibit.
A developer generates the base scaffolding for an API in Anypoint Studio.
Which HTTP status code is returned while testing using the API Kit console if no values are entered in client-secret?
- A. HTTP status code:500
- B. HTTP status code:200
- C. HTTP status code:403
- D. HTTP status code:400
Answer: C
Explanation:
Based on the code snippet and schema.json file below, when testing using the API Kit console if no values are entered in client-secret, HTTP status code 403 (FORBIDDEN) is returned. This is because client-secret is defined as a required header parameter in schema.json file, which means that it must be present in every request. If no values are entered in client-secret, then it is equivalent to omitting this header parameter, which violates the schema and causes APIKit Router to return HTTP status code 403. Reference: https://docs.mulesoft.com/apikit/4.x/apikit-4-headers
NEW QUESTION # 36
Refer to the exhibit.
A Mute Object Store is configured with an entry TTL of one second and an expiration interval of 30 seconds.
What is the result of the flow if processing between os'store and os:retrieve takes 10 seconds?
- A. OS:KEY_NOT_FOUND
- B. originalPayload
- C. testPayload
- D. nullPayload
Answer: D
Explanation:
The result of the flow is nullPayload if processing between os:store and os:retrieve takes 10 seconds. This is because the entry TTL of the object store is one second, which means that any stored value expires after one second and is removed from the object store. The expiration interval of 30 seconds only determines how often the object store checks for expired values, but it does not affect the TTL. Therefore, when os:retrieve tries to get the value after 10 seconds, it returns nullPayload because the value has already expired and been removed. Reference: https://docs.mulesoft.com/object-store/osv2-faq#how-does-the-time-to-live-work
NEW QUESTION # 37
What is the MuleSoft recommended method to encrypt sensitive property data?
- A. The encryption key and sensitive data should be different for each environment
- B. The encryption key should be identical for all environments
- C. The encryption key should be different for each environment and the sensitive data should be the same for all environments
- D. The encryption key should be identical for all environments and the sensitive data should be different for each environment
Answer: A
Explanation:
The MuleSoft recommended method to encrypt sensitive property data is to use the Secure Properties Tool that comes with Anypoint Studio. This tool allows encrypting properties files with a secret key and then decrypting them at runtime using the same key. The encryption key and sensitive data should be different for each environment to ensure security and avoid accidental exposure of sensitive data. Reference: https://docs.mulesoft.com/mule-runtime/4.3/secure-configuration-properties
NEW QUESTION # 38
A Mule implementation uses a HTTP Request within an Unit Successful scope to connect to an API.
How should a permanent error response like HTTP:UNAUTHORIZED be handle inside Until Successful to reduce latency?
- A. Configure retrying until a MULERETRY_EXHAUSTED error is raised or the API responds back with a successful response.
- B. Put the HTTP Request inside a try scope in Unit Successful.
In the error handler, use On Error Propagate to catch permanent errors like HTTP UNAUTHORIZED. - C. Put the HTTP Request inside a try scope in Unit Successful.
In the error handler, use On Error Continue to catch permanent errors like HTTP UNAUTHORIZED. - D. In Until Successful configuration, set the retry count to 1 for error type HTTP: UNAUTHORIZED.
Answer: C
Explanation:
To handle a permanent error response like HTTP:UNAUTHORIZED inside Until Successful, the developer should put the HTTP Request inside a try scope in Unit Successful, and use On Error Continue to catch permanent errors like HTTP UNAUTHORIZED in the error handler. This way, the developer can avoid retrying requests that will always fail due to a permanent error, and reduce latency. On Error Continue allows the flow to continue processing after handling the error. Reference: https://docs.mulesoft.com/mule-runtime/4.3/until-successful-scope https://docs.mulesoft.com/mule-runtime/4.3/on-error-continue-concept
NEW QUESTION # 39
The Center for Enablement team published a common application as a reusable module to the central Nexus repository.
How can the common application be included in all API implementations?
- A. Add a Maven dependency in the PCM file with multiple-plugin as <classifier>
- B. Copy the common application's source XML file and out it in a new flow file in the src/main/mule folder
- C. Download the common application from Naxus and copy it to the src/main/resources folder in the API
- D. Add a Maven dependency in the POM file with jar as <classifier>
Answer: D
Explanation:
To include a common application as a reusable module in all API implementations, the developer should add a Maven dependency in the POM file with jar as <classifier>. This way, the developer can reuse Mule code from another application by packaging it as a JAR file and adding it as a dependency in the POM file of the API implementation. The classifier element specifies that it is a JAR file. Reference: https://docs.mulesoft.com/mule-runtime/4.3/mmp-concept#add-a-maven-dependency-to-the-pom-file
NEW QUESTION # 40
A Mule application deployed to a standardalone Mule runtime uses VM queues to publish messages to be consumed asynchronously by another flow.
In the case of a system failure, what will happen to in-flight messages in the VM queues that have been consumed?
- A. For any type of queue, the message will be lost
- B. For transient queues, the message will be processed after the system comes online
- C. For nay type of queue, the message will be processed after the system comes online
- D. For persistent queues, the message will be processed after the system comes online
Answer: D
Explanation:
In case of a system failure, in-flight messages in persistent VM queues that have been consumed will be processed after the system comes online. This is because persistent VM queues store messages on disk and guarantee delivery even if there is a system crash or restart. Therefore, any in-flight messages that have been consumed but not processed will be recovered from disk and processed when the system is back online. Reference: https://docs.mulesoft.com/mule-runtime/4.3/vm-connector#persistent-queues
NEW QUESTION # 41
Mule application A is deployed to CloudHub and is using Object Store v2. Mute application B is also deployed to CloudHub.
Which approach can Mule application B use to remove values from Mule application A'S Object Store?
- A. CloudHub REST API
- B. CloudHub Connector
- C. Object Store v2 REST API
- D. Object Store Connector
Answer: C
Explanation:
To remove values from Mule application A's Object Store v2, Mule application B can use Object Store v2 REST API. This API allows performing operations on Object Store v2 resources using HTTP methods, such as GET, POST, PUT, and DELETE. Mule application B can use the DELETE method to remove values from Mule application A's Object Store v2 by specifying the object store ID and the key of the value to delete. Reference: https://docs.mulesoft.com/object-store/osv2-apis
NEW QUESTION # 42
A healthcare portal needs to validate the token that it sends to a Mule API. The developer plans to implement a custom policy using the HTTP Policy Transform Extension to match the token received in the header from the heathcare portal.
Which files does the developer need to create in order to package the custom policy?
- A. JSON properties file, XML template file
- B. JSON properties file, YAML configuration file
- C. XML template file, YAML configuration file
- D. Deployable ZIP file, YAML configuration file
Answer: C
Explanation:
To package a custom policy using the HTTP Policy Transform Extension, the developer needs to create an XML template file and a YAML configuration file. The XML template file defines the policy logic using Mule components and placeholders for user-defined properties. The YAML configuration file defines the metadata of the policy, such as its name, description, category, parameters, and dependencies. Reference: https://docs.mulesoft.com/api-manager/2.x/http-policy-transform#packaging-the-policy
NEW QUESTION # 43
In a Mule project, Flow-1 contains a flow-ref to Flow-2 depends on data from Flow-1 to execute successfully.
Which action ensures the test suites and test cases written for Flow-1 and Flow-2 will execute successfully?
- A. Chain together the test suites and test cases for Flow-1 and Flow-2
- B. Use ''Before Test Case'' To collect data from Flow-1 test cases before running Flow-2 test cases
- C. Use 'After Test Case' to produce the data needed from Flow-1 test cases to pass to Flow-2 test cases
- D. Use ''Set Event to pass the input that is needed, and keep the test cases for Flow-1 and Flow-2 independent
Answer: D
Explanation:
To ensure the test suites and test cases written for Flow-1 and Flow-2 will execute successfully, the developer should use a Set Event processor to pass the input that is needed by Flow-2, and keep the test cases for Flow-1 and Flow-2 independent. This way, the developer can isolate the testing of each flow and avoid coupling them together. Reference: https://docs.mulesoft.com/munit/2.3/munit-test-flow
NEW QUESTION # 44
Which pattern can a web API use to notify its client of state changes as soon as they occur?
- A. ETL data load
- B. Schedule Event Publisher
- C. Shared database trigger
- D. HTTP Webhock
Answer: D
Explanation:
A web API can use HTTP Webhook to notify its client of state changes as soon as they occur. A webhook is an HTTP callback that allows an API to send real-time notifications to another system or application when an event happens. The client registers a URL with the API where it wants to receive notifications, and then the API sends an HTTP request to that URL with information about the event. Reference: https://docs.mulesoft.com/connectors/webhook/webhook-connector
NEW QUESTION # 45
Multiple individual Mute application need to use the Mule Maven plugin to deploy to CloudHub.
The plugin configuration should .. reused where necessary and anything project, specific should be property-based.
Where should the Mule Maven details be configured?
- A. Settings, xml
- B. Pom, xml
- C. A parent pom.xml
- D. A Bill of Materials (BOM) parent pm
Answer: C
Explanation:
To reuse Mule Maven plugin configuration across multiple individual Mule applications, the developer should use a parent pom.xml file. A parent pom.xml file defines common configuration for one or more child projects that inherit from it. The developer can specify common properties and dependencies for all child projects in the parent pom.xml file, such as Mule Maven plugin configuration, and then reference them in each child project's pom.xml file using placeholders. Reference: https://docs.mulesoft.com/mule-runtime/4.3/mmp-concept#parent-pom https://maven.apache.org/guides/introduction/introduction-to-the-pom.html#Project_Inheritance
NEW QUESTION # 46
Refer to the exhibit.
A Mule application pom.xml configures the Maven Resources plugin to exclude parsing binary files in the project's src/main/resources/certs directory.
Which configuration of this plugin achieves a successful build?
- A.

- B.

- C.

- D.

Answer: A
Explanation:
To configure the Maven Resources plugin to exclude parsing binary files in the project's src/main/resources/certs directory, option C should be used. This option specifies that any files with .cer or .jks extensions under the certs directory should be excluded from filtering. Filtering is a process of replacing placeholders with actual values in resource files during the build process. Binary files should not be filtered because they may become corrupted or unusable. Reference: https://maven.apache.org/plugins/maven-resources-plugin/examples/filter.html https://maven.apache.org/plugins/maven-resources-plugin/examples/include-exclude.html
NEW QUESTION # 47
A developer is working on a project that requires encrypting all data before sending it to a backend application. To accomplish this, the developer will use PGP encryption in the Mule 4 Cryptography module.
What is required to encrypt the data before sending it to the backend application?
- A. The application needs the private key from the backend service to encrypt the data
- B. The application needs to configure HTTPS TLS context information to encrypt the data
- C. The application needs to both the private and public keys to encrypt the data
- D. The application needs the public key from the backend service to encrypt the data
Answer: D
Explanation:
To encrypt the data before sending it to the backend application using PGP encryption, the application needs the public key from the backend service. PGP encryption uses a public-key cryptography system, which means that each party has a pair of keys: a public key and a private key. The public key is used to encrypt data, and the private key is used to decrypt data. Therefore, to encrypt data for a specific recipient (the backend service), the application needs to use the recipient's public key. The recipient can then use its own private key to decrypt the data. Reference: https://docs.mulesoft.com/mule-runtime/4.3/cryptography-pgp
NEW QUESTION # 48
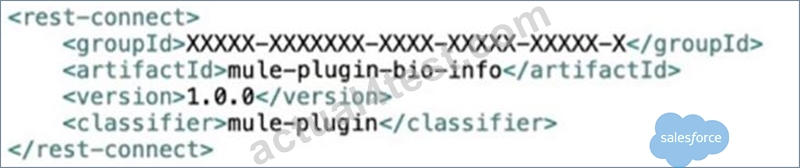
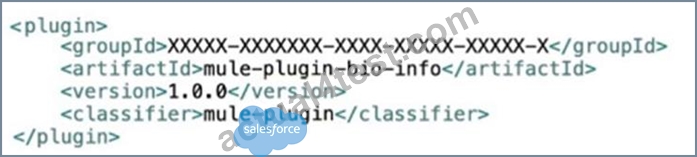
Refer to the exhibits.
Bioinfo System API is implemented and published to Anypoint Exchange. A developer wants to invoke this API using its REST Connector.
What should be added to the POM?
- A.

- B.

- C.
- D.

- E.
Answer: E
Explanation:
To invoke Bioinfo System API using its REST Connector, option E should be added to the pom.xml file. This option adds a dependency for Bioinfo System API REST Connector with its group ID, artifact ID, version, classifier, and type. The classifier specifies that it is a REST Connector (raml-client), and the type specifies that it is a Mule plugin (mule-plugin). Reference: https://docs.mulesoft.com/apikit/4.x/apikit-4-generate-from-rest-api-task#add-the-api-dependency-to-the-pom-file
NEW QUESTION # 49
A developer deploys an API to CloudHub and applies an OAuth policy on API Manager. During testing, the API response is slow, so the developer reconfigures the API so that the out-of-the-box HTTP Caching policy is applied first, and the OAuth API policy is applied second.
What will happen when an HTTP request is received?
- A. In case of a cache miss, only the HTTP Caching policy is evaluated; then the API retrieves the data from the API implementation, and the policy stores the data to be cached in Object Store
- B. In case of a cache it, only the HTTP Caching policy is evaluating; then the cached response is returned to the caller
- C. In case of a cache hit, both the OAuth and HTTP Caching policies are evaluated; then the cached response is returned to the caller
- D. In case of a cache miss, both the OAuth and HTTP Caching policies are evaluated; then the API retrieves the data from the API implementation, and the policy does not store the data in Object Store
Answer: B
Explanation:
When an HTTP request is received and the HTTP Caching policy is applied first, it checks if there is a cached response for that request in Object Store. If there is a cache hit, meaning that a valid cached response exists, then only the HTTP Caching policy is evaluated and the cached response is returned to the caller without invoking the OAuth policy or the API implementation. If there is a cache miss, meaning that no valid cached response exists, then both the HTTP Caching policy and the OAuth policy are evaluated before invoking the API implementation. Reference: https://docs.mulesoft.com/api-manager/2.x/http-caching-policy#policy-ordering
NEW QUESTION # 50
A developer has created the first version of an API designed for business partners to work commodity prices.
What should developer do to allow more than one major version of the same API to be exposed by the implementation?
- A. In Anypoint Studio, generate scaffolding from the RAML, and the modify the <http:listerner> in the generated flows to include a parameter to replace the version number
- B. In Design Center, open the RAML and modify baseUn to include a variable that indicates the version number
- C. In Design Center, open the RAML and modify each operation to include the major version number
- D. In Anypoint Studio, generate scaffolding from the RAML, and then modify the flow names generated by APIKit to include a variable with the major version number
Answer: B
Explanation:
To allow more than one major version of the same API to be exposed by the implementation, the developer should modify the baseUri property in the RAML file to include a variable that indicates the version number. The baseUri property defines the base URL of the API and can include variables that are replaced with actual values when mocking or deploying the API. By using a variable for the version number, the developer can expose different versions of the API using different base URLs and avoid conflicts or confusion. Reference: https://docs.mulesoft.com/api-designer/design-modify-raml-specs#baseuri https://docs.mulesoft.com/api-manager/2.x/api-versioning
NEW QUESTION # 51
Which configurations are required for HTTP Listener to enable mTLS authentication?
- A. Set an appropriate keystore configuration and use persistent connections for the listener
- B. Set an appropriate keystore and truststore configuration for the listener
- C. Set an appropriate reconnection strategy and use persistent connections for the listener
- D. Set an appropriate truststore configuration and reconnection strategy for the listener
Answer: B
Explanation:
To enable mTLS authentication for HTTP Listener, the developer needs to set an appropriate keystore and truststore configuration for the listener. The keystore contains the certificate and private key of the Mule application that are used to prove its identity to clients. The truststore contains the certificates of trusted clients that are allowed to access the Mule application. Reference: https://docs.mulesoft.com/mule-runtime/4.3/tls-configuration#mutual-authentication
NEW QUESTION # 52
A company deploys 10 public APIs to CloudHub. Each API has its individual health endpoint defined. The platform operation team wants to configure API Functional Monitoring to monitor the health of the APIs periodically while minimizing operational overhead and cost.
How should API Functional Monitoring be configured?
- A. From one private location with all 10 APIs in a single schedule
- B. From 10 public locations with each API in its own schedule
- C. From one public location with all 10 APIs in a single schedule
- D. From one public location with each API in its own schedule
Answer: C
Explanation:
To configure API Functional Monitoring to monitor the health of 10 public APIs periodically while minimizing operational overhead and cost, the developer should use one public location with all 10 APIs in a single schedule. A public location is a worker that runs in a CloudHub shared environment, which is cheaper and easier to maintain than a private location. A single schedule allows running all 10 APIs tests at the same time and frequency, which reduces complexity and resource consumption. Reference: https://docs.mulesoft.com/functional-monitoring/fm-create-monitor#create-a-monitor
NEW QUESTION # 53
Which statement is true about using mutual TLS to secure an application?
- A. Mutual TLS requires a hardware security module to be used
- B. Mutual TLS authenticates the identity of the server before the identity of the client
- C. Mutual TLS ensures only authorized end users are allowed to access an endpoint
- D. Mutual TLS increases the encryption strength versus server-side TLS alone
Answer: B
Explanation:
Mutual TLS (mTLS) is an extension of TLS that requires both parties (client and server) to present their certificates to each other during the handshake process. This way, both parties can verify each other's identity and establish a secure connection. The authentication of the server happens before the authentication of the client, as the server sends its certificate first and then requests the client's certificate. Reference: https://docs.mulesoft.com/mule-runtime/4.3/tls-configuration#mutual-authentication
NEW QUESTION # 54
A Mule application for processing orders must log the order ID for every log message output.
What is a best practice to enrich every log message with the order ID?
- A. Create a custom XML SDK component to wrap the logger processor and automatically add the order ID within the connector
- B. Set a flow variable and edit the log4/2.xml file to output the variable as part of the message pattern
- C. Use flow variables within every logger processor to log the order ID
- D. Use the Tracing module to set logging variables with a Mapped Diagnostic Context
Answer: D
Explanation:
To enrich every log message with the order ID, the developer should use the Tracing module to set logging variables with a Mapped Diagnostic Context (MDC). The Tracing module allows adding custom key-value pairs to log messages using MDC variables. The developer can use Set Logging Variables operation to set the order ID as an MDC variable and then use it in any logger processor within the same thread or event. Reference: https://docs.mulesoft.com/tracing-module/1.0/tracing-module-reference#set-logging-variables
NEW QUESTION # 55
The flow is invoicing a target API. The API's protocol is HTTPS. The TLS configuration in the HTTP Request Configuration global element is set to None. A web client submits a request to http:localhost:8081/vehicles.
If the certificate of the target API is signed by a certificate authority (CA), what is true about the HTTP Request operation when the flow executes?
- A. The HTTP Request operation will succeed if the CA's certificate is present in the JRE's default truststore.
- B. The HTTP Request operation will always fail regardless of the CA
- C. The HTTP Request operation will succeed if the CA'S certificate is present in the JRE's default keystore
- D. The HTTP Request operation will always succeed regardless of the CA
Answer: A
Explanation:
The HTTP Request operation will use the default truststore of the JRE to validate the certificate of the target API. If the CA's certificate is present in the truststore, the operation will succeed. Otherwise, it will fail with a handshake exception. Reference: https://docs.mulesoft.com/mule-runtime/4.3/tls-configuration#tls-default
NEW QUESTION # 56
......
Latest Questions Salesforce-MuleSoft-Developer-II Guide to Prepare Free Practice Tests: https://examtorrent.actual4test.com/Salesforce-MuleSoft-Developer-II_examcollection.html